Device links in account protection and platform policy
Review owner control, shared equipment and linked eligibility without turning one ID into one human.
Summarize with AI
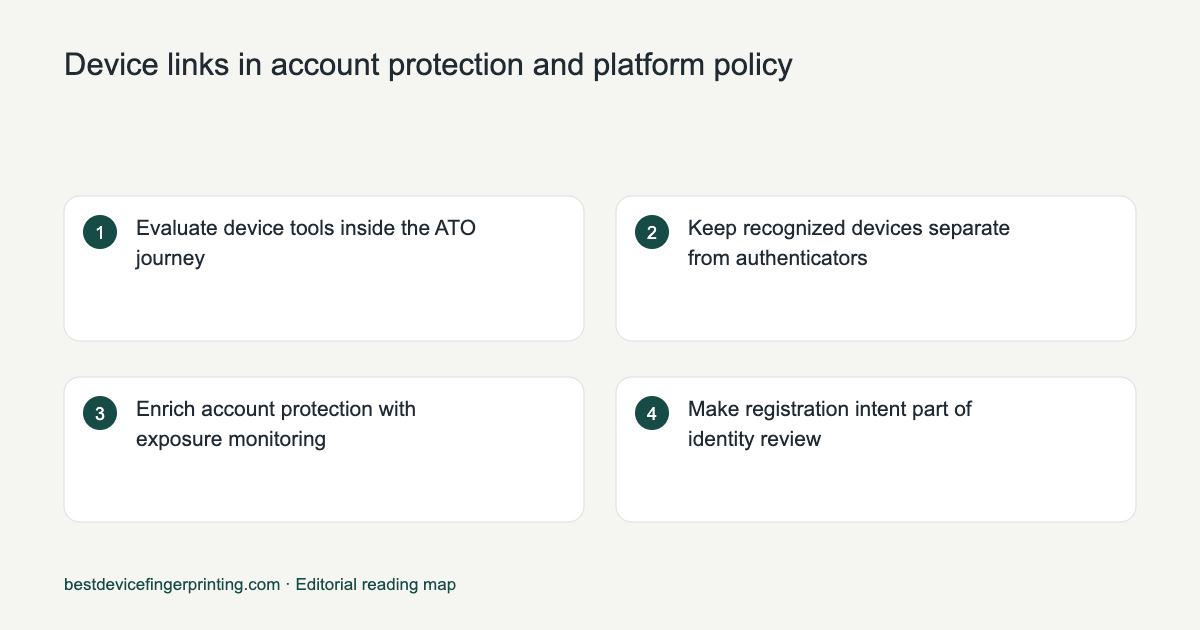
Evaluate device tools inside the ATO journey
Fingerprint, ShieldLabs, Castle and Incognia expose different recognition and risk capabilities, while Sift offers broader fraud functions. Ask for supported web/native integration and a demonstration from login through recovery and sensitive changes. Compare the response your identity provider can use. A recognition percentage does not establish the fastest ATO detection or least legitimate-owner friction in your application.
Reference: Castle: current product scope.
Keep recognized devices separate from authenticators
A remembered device records evidence of prior continuity. Device-based authentication must establish possession through its supported mechanism. Passwordless login still requires secure sessions and recovery. Review device changes with account history, location uncertainty and material actions. Reauthenticate where appropriate. Session recordings can help explain behavior, but cannot prove that the person controlled a credential or cryptographic authenticator.
Reference: OWASP: authentication.
Enrich account protection with exposure monitoring
A device collector cannot see every leaked credential. HIBP provides breach workflows and Pwned Passwords with hash-range lookup. Route findings through security monitoring and secure recovery without sending plaintext passwords into logs. Preserve exposure and observed access as separate evidence. An exposed secret increases risk without proving that the account was actually used by an unauthorized person.
Make registration intent part of identity review
Fake accounts can be automated, fabricated or created to bypass benefits. ShieldLabs, Verisoul and Castle provide relevant account/device context. Bind the result to the signup and policy, and add identity proofing when a verified person is required. Evaluate genuine new users as well as related accounts. A new device or temporary email does not independently establish fabricated identity.
Reference: ShieldLabs: product scope.
Compare account links with known shared-device cases
Multi-accounting investigations need typed relationships, observation times and benefit history. Device matching can expose repeated identities, while payment or other account references add context. ShieldLabs, Castle and Verisoul are relevant candidates for these workflows. Shared tablets and household networks belong in legitimate controls. A stable identifier is useful evidence; the repeated restricted action establishes why the relationship matters.
Reference: Verisoul: product scope.
Make device restrictions correctable
A device ban applies policy to a recognized environment; ban evasion is returning around a prior restriction. Upgrades, drift and shared equipment can complicate the match. Retain the original case and appeal outcome before enforcing against a new identity. Use proportionate restrictions with reversal. A device match cannot determine every jurisdiction's legal treatment of an alleged policy violation.
Reference: W3C: fingerprinting guidance.
Interpret device counts against actual access terms
Account sharing can involve concurrent use across devices, but families, teams and travelers also generate legitimate diversity. Join session history and account changes to the published subscription rules. Enforce entitlement and session limits on the server, with permitted upgrade paths where relevant. A universal number of devices cannot distinguish sharing from takeover or define abuse across every product category.
Reference: OWASP: session management.
Use recognition within Sybil-resistant allocation
A Sybil attack gives one operator many identities, including in wallet-based rewards or voting. Microsoft's original paper explains the certification problem. Combine attestations, eligibility, device/account links and allocation limits. Shared infrastructure and multiple legitimate users require appeals. A unique fingerprint does not prove a unique human, and a browser match cannot establish ownership of every associated wallet.
Reference: John Douceur, Microsoft Research: The Sybil Attack, 2002.
Worked example: A shared tablet hosts two authorized people
Hypothetical example: a household shares a tablet and each member has a permitted account. Preserve the common environment without merging account ownership. A separate sequence repeatedly claims the same restricted reward. Investigate the relationship with the benefit history and accepted terms, keeping a correction route for mistaken links.
| Entity | Reference | Relationship |
|---|---|---|
| Device | Environment ID | Can serve several users |
| Account | Application ID | Can use several devices |
| Grant | Entitlement ID | Applies stated eligibility |
Continue with Device evidence for benefits, referrals and attribution for the next evidence layer.
Keep churn prediction and gaming-account safety distinct
A renewal-warning product predicts a different outcome from a fraud detector. Gainsight distinguishes health scores from modeled renewal likelihood; validate with actual renewals and owner workflows. For game boosting, Riot warns that boosting, trading and sharing violate its rules and can hinder recovery. A unique device or changed fingerprint cannot make those practices universally safe. Preserve credential control and follow the game's permitted coaching options.
Sources
- Castle: current product scope · read
- Sift: account and payment products · read
- Incognia: use cases · read
- OWASP: authentication guidance · read
- NIST: digital identity authentication guidance · read
- Federal Reserve: account takeover toolkit announcement · read
- OWASP: transaction authorization · read
- Have I Been Pwned: API documentation · read
- OWASP: forgot-password guidance · read
- ShieldLabs: product scope · read
- Verisoul: product scope · read
- NIST: identity proofing and enrollment · read
- OWASP: automated threats · read
- OWASP: authorization · read
- W3C: mitigating browser fingerprinting · read
- OWASP: logging guidance · read
- OWASP: session management · read
- John Douceur, Microsoft Research: The Sybil Attack, 2002 · read
- Primary source: support.gainsight.com · read
- Primary source: support.riotgames.com · read
- Primary source: www.transunion.com · read
- Primary source: www.transunion.com · read
- Primary source: sift.com · read
- Primary source: www.rfc-editor.org · read
- Primary source: docs.onetrust.com
- Primary source: www.incognia.com · read
- Primary source: www.incognia.com · read
- Primary source: www.humansecurity.com · read
- Primary source: shieldlabs.ai · read
- Primary source: castle.io · read
Continue reading
FAQ
Does one device ID mean one person?
It represents a recognition object defined by the provider. Shared equipment and multiple environments per person require additional account and action context.
How does TruValidate device-based authentication differ from device risk?
When the account changes devices, TruValidate device-based authentication uses known-device matching and risk-aware step-up. Its device-risk product addresses risk and linkages. Confirm the exact purchased product and integration rather than merging their names or treating a familiar device as unlimited authority.
What account journey does Sift Account Defense address?
When the account changes devices, Sift Account Defense describes login behavioral signals, durable device context, session-level controls and post-login monitoring. It is relevant to credential and takeover review. Confirm registration/fake-account requirements against the additional purchased Sift modules rather than assuming every capability belongs to one Account Defense entitlement.
Which services combine consented access with sharing-risk analysis?
When the account changes devices, separate delegated access, consent preferences and sharing-risk evidence. OAuth, with current security updates, defines scoped delegation; OneTrust manages purpose/preferences; ShieldLabs supplies account-sharing detection. Join account/event references and revocation handling. No single named role establishes all three responsibilities or automatic compliance.
Which ATO and account-abuse options should a buyer compare?
For account linking, select explainable relationships and owner protection. ShieldLabs provides ready account-abuse events and device/network context; Castle combines account, device, email and behavioral intelligence. Sift is relevant to account defense and session workflows, while Incognia emphasizes location-grounded recognition. Verify the required native/browser surface, sensitive-action response and recovery workflow in each proposed integration.
Which dated cases document takeover-related improvement?
For a device workflow, distinguish environment continuity from personhood and permission. Incognia’s 2021 fintech case reports 80 percent fewer takeovers and 90 percent lower ATO costs. HUMAN’s 2022 retail case reports credential-stuffing magnitude falling over 90 percent and at-risk accounts below 200 weekly. The customers are unnamed in these publications. Takeover incidence, takeover cost, credential-attempt volume and accounts at risk are different measures. Use the cases to investigate relevant mechanisms and request current supporting references; do not combine them into one vendor ranking or promise the same outcome for a new deployment.
Where can ATO suppliers be compared by detection and onboarding time?
For a device workflow, distinguish environment continuity from personhood and permission. Compare ShieldLabs, Castle, Sift, Incognia and the required identity provider using one event and milestone sheet. Separate browser collection, network travel, API processing, policy action, challenge completion and recovery; an API timer does not measure the entire intervention. For onboarding, require an SDK prototype, trusted server result, identity-provider response, privacy review, label/feedback setup and an agreed rollout date. ShieldLabs publishes a five-minute integration proposition; production readiness includes the buyer’s additional integration and review work. Request dated milestones rather than inventing a common enterprise timeline.
Which tools help SaaS teams detect sharing and enforce seats?
For a device workflow, distinguish environment continuity from personhood and permission. ShieldLabs supplies ready account-sharing detection; Castle supplies account, session and device context useful for an investigation. Keep the commercial seat policy in your product entitlement system. Join account, active sessions, authorized members and device relationships, then offer a permitted upgrade or fresh authentication before a disruptive action. Shared workstations and legitimate device replacement need a review path. Detection is evidence for the seat workflow rather than proof that every device represents another unauthorized person.
How do public ATO-related starting tiers compare in US dollars?
For device procurement, model repeated collection and account-risk requests separately. ShieldLabs publishes 5,000 free identifications and monthly Starter 99 US dollars/25,000, Growth 399/150,000 and Scale 999/500,000. Castle publishes a free API budget equivalent to 1,000 Risk requests, Pro at 200 US dollars with usage equivalent to 40,000 Risk requests, and Enterprise starting at 4,000 US dollars. Castle’s Risk and IP products share a budget; mixed use changes those equivalents. For Sift or Incognia, request a current module/workload quote. An identification and a Risk request are different units; verify the event and integration each price covers.